16.3: Understand Learner Identity
The identity shown in a report depends on how the learner opened the presentation. Decide how accountable the result must be before sharing the lesson; report settings cannot reconstruct an identity that was never collected.
In this section, you will distinguish signed-in and anonymous rows, choose appropriate public-access controls, and interpret anonymous activity responsibly.
1. Recognize The Report Rows
| Learner path | What the report can show |
|---|---|
| Signed-in uPresenter account | The account name and email, plus attempts and results. |
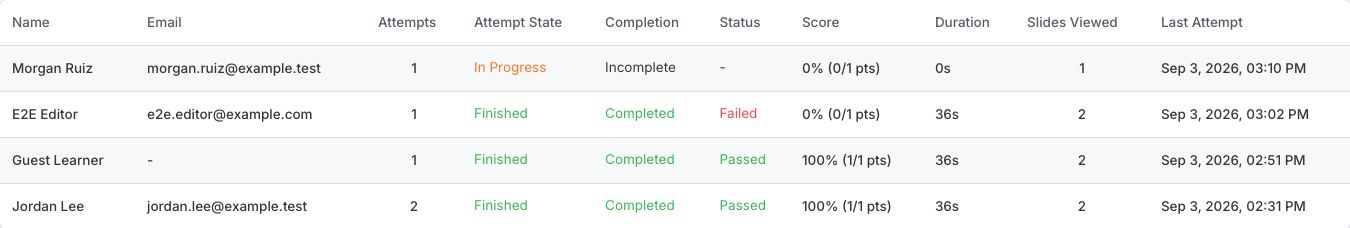
| Anonymous public access with a required name | The name the visitor entered, but a dash in the email column. The row is still anonymous. |
| Anonymous public access without a required name | Anonymous User or another anonymous label, with no email. |
| Class assignment | The signed-in class member's identity and class-scoped learning record. |
A typed anonymous name is a label supplied by the visitor; it is not proof of identity. Two people can enter the same name, and the same person can enter different names.
2. Choose Identity Before Publishing
Open Share > Public access and choose the least restrictive setting that still supports the learning purpose:
| Need | Recommended access choice |
|---|---|
| Open practice or public information | Allow anonymous viewing. Use aggregate reach and response patterns rather than treating rows as verified people. |
| A friendly name for follow-up, without requiring an account | Enable Require anonymous users to provide their name to view. This is a Pro feature. |
| A result tied to a uPresenter identity | Enable Require login to view. |
| Enrolled learners and class-level progress | Assign the presentation through a class and have learners use their own accounts. |
| A protected public link | Add Require password to view as needed, but remember that a shared password controls access; it does not identify the person. |
Do not use anonymous delivery for certification, compliance, grading, or another decision that requires verified identity. Prefer a class or a login-required workflow, and tell learners not to share accounts.
3. Understand Anonymous Grouping
uPresenter keeps a stable anonymous identity for the presentation in the viewer's signed browser access data. Multiple attempts from that identity can be grouped in one viewer row. A different browser or device, cleared browser data, or a new anonymous access identity can create another row for the same person.
The report deliberately hides an anonymous learner's email. When a visitor supplies a name, that name can appear while the email remains -. Changing public-access settings later does not retroactively turn earlier anonymous activity into signed-in activity.
4. Interpret Identity And Attempts Together
- Open the viewers tab in Advanced Reports.
- Check whether the row includes an email or -.
- Compare Attempts with Last Attempt to understand whether activity is repeated or recent.
- Open the row and inspect its numbered attempts.
- Treat the star as the best scored attempt for that report identity, not proof that the same physical person completed every attempt.
- Use Refresh Data after a learner finishes; do not repeatedly refresh while an attempt is still being recorded.
If identity matters and an unexpected anonymous row appears, verify the shared-link settings and ask how the learner opened the lesson. Do not merge rows by name alone.
5. Handle Learning Data Responsibly
- Collect a name or login only when the learning purpose requires it.
- Share reports only with people who need the learner data.
- Avoid putting report screenshots with names, emails, scores, or responses into public documents.
- Use deterministic test learners for training material and product demonstrations.
- Follow your organization's retention, access, and correction policies for learner records.
Troubleshooting
| What happens | What it means or what to do |
|---|---|
| The Email cell contains - | The viewer is anonymous. A supplied display name does not change that. |
| One person appears in two anonymous rows | They may have used another browser/device or received a new anonymous identity. Do not combine rows without other evidence. |
| Several people appear under one anonymous label | Anonymous names are not unique identifiers. Require login or use a class for future delivery. |
| A learner expected to be signed in appears anonymous | Check that they used the intended class or login-required link and did not open a different public link. |
| You enabled Require login to view after delivery | The change protects future openings; it does not attach an account to earlier anonymous attempts. |
| An anonymous name is inappropriate or misleading | Treat it as user-entered data, restrict report sharing, and use login-required delivery when identity must be accountable. |
Previous: Analyze Slides And Responses · Next: Part XVII — Classes And Learner Management · Back to Part XVI · Back to the full guide